Security tooling you can actually run.
Small, dependency-free tools and plain-language write-ups for the vulnerabilities that matter this week. Built in the open by the AdZoic team.
Latest posts
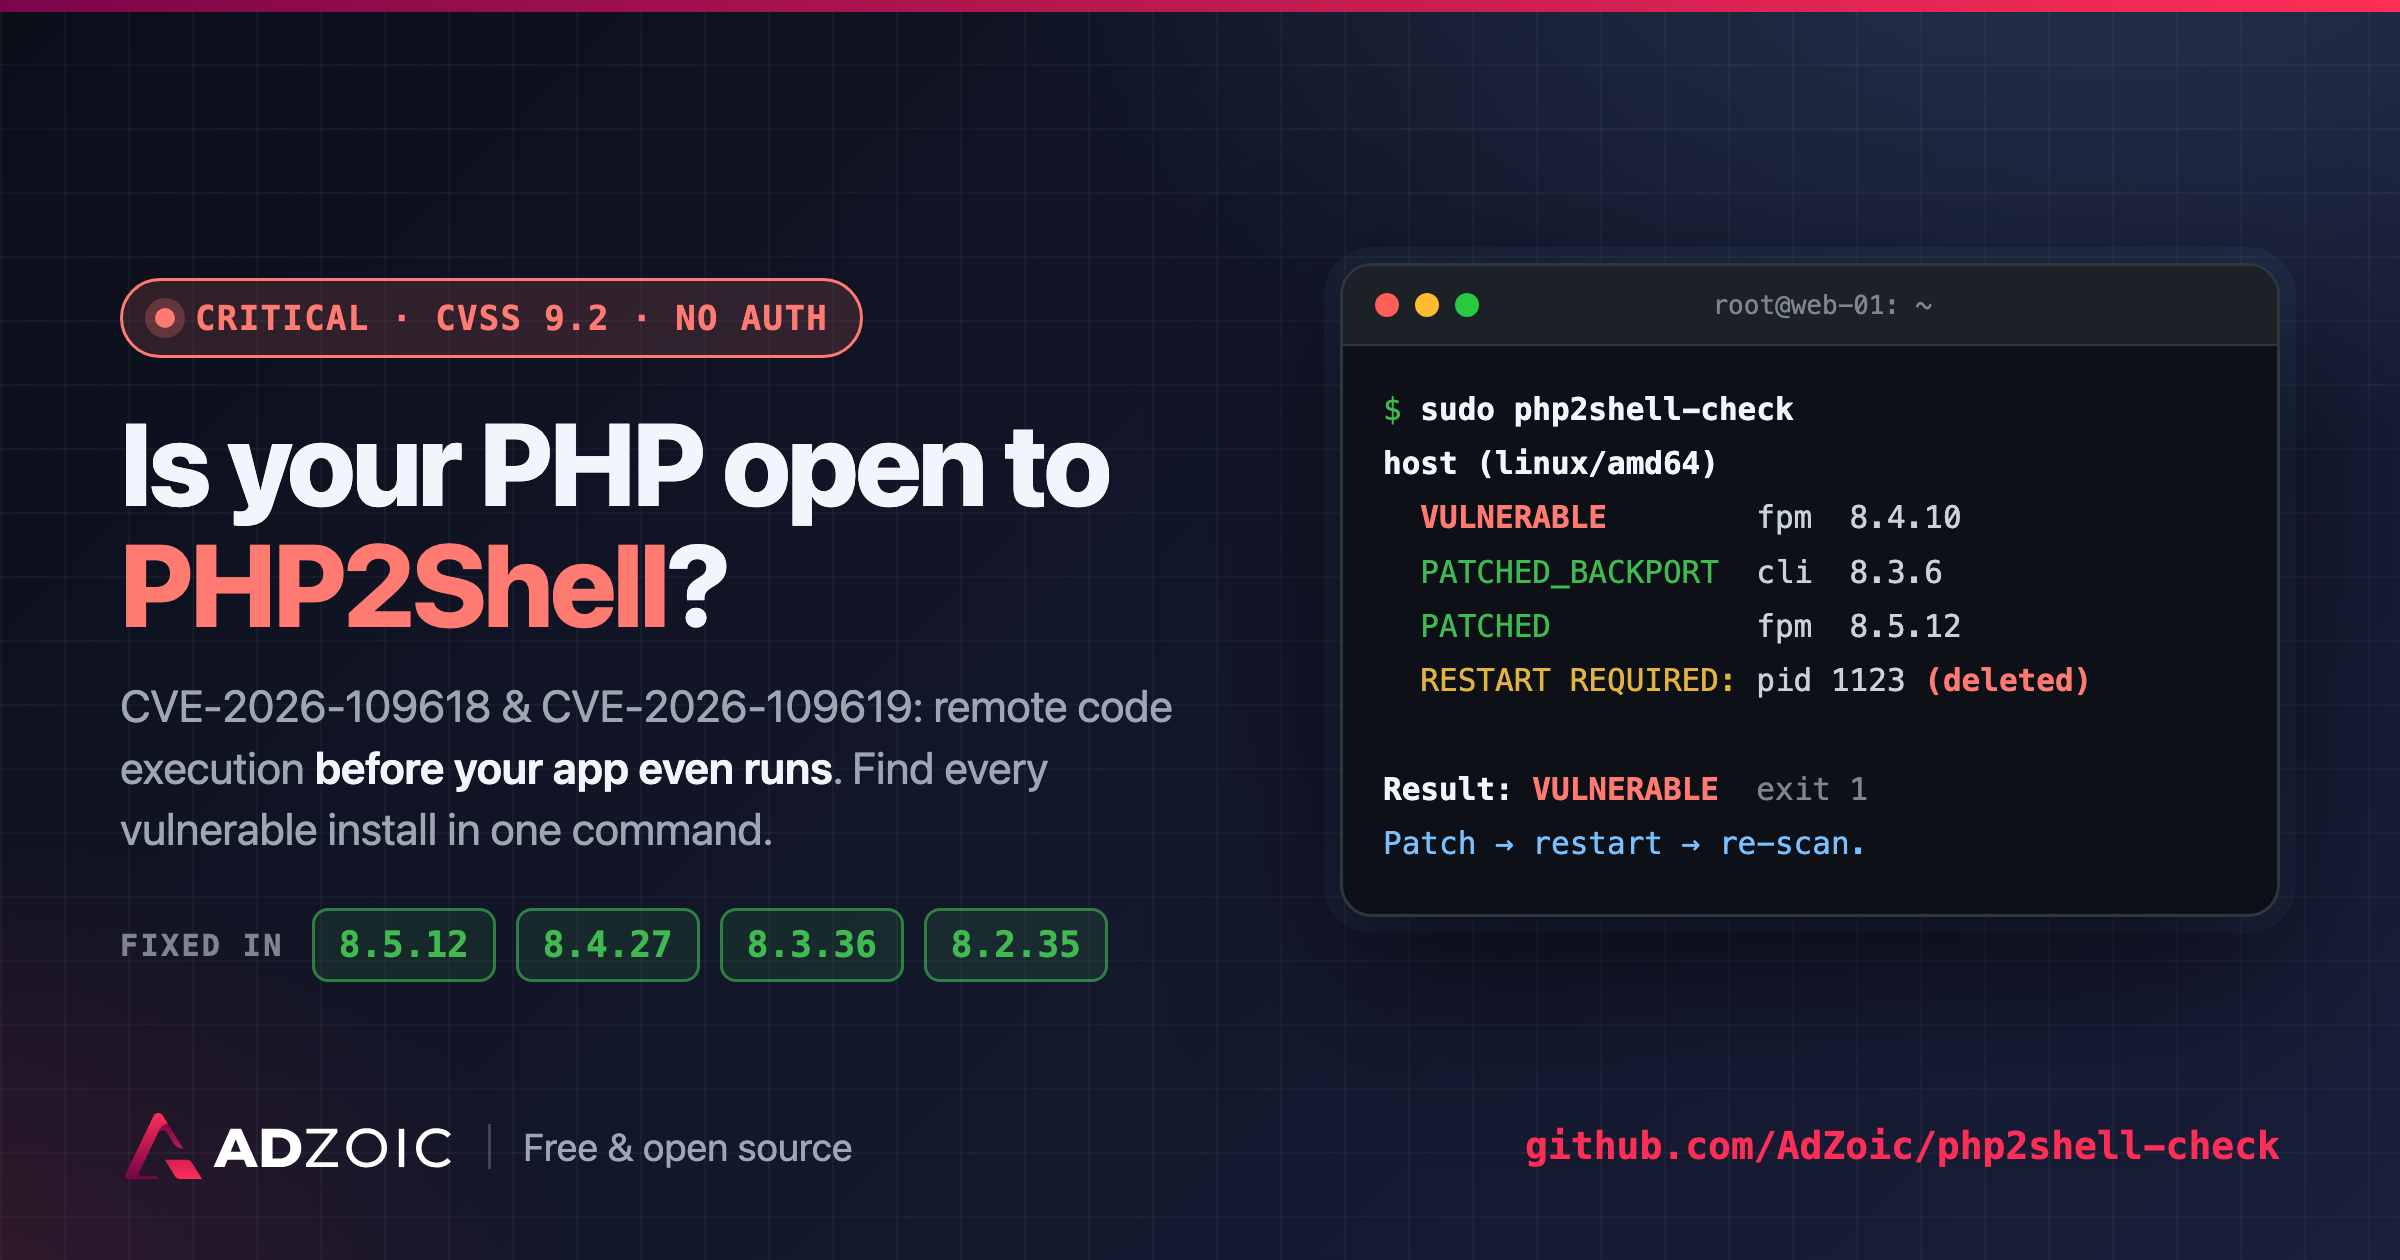
PHP2Shell: find every vulnerable PHP install in one command
We built php2shell-check, a free single-binary scanner that finds every PHP runtime on a server or container image, tells you if it is exposed to PHP2Shell, and what to do next.
Read post →Engineering at AdZoic
How we build and run our ad platform. These posts live on adzoic.com.
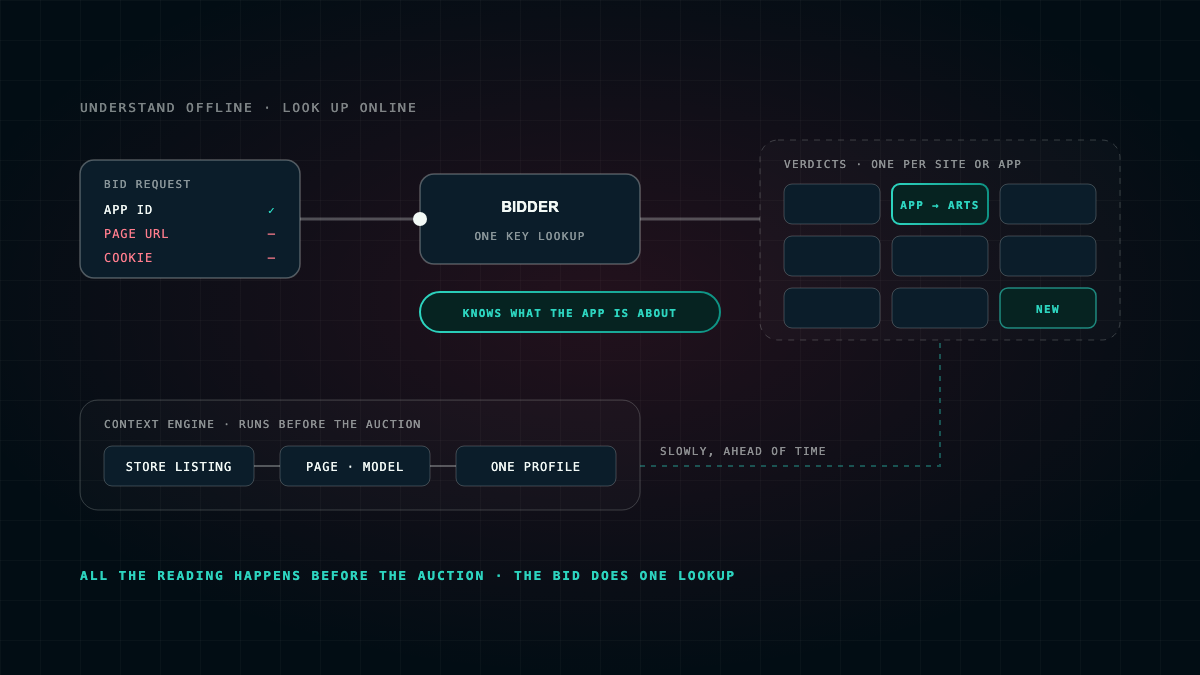
Contextual targeting without cookies: how we rebuilt our context engine
Every ad decision now knows what a page or app is about in a fraction of a millisecond, with no user identifier. The five design decisions that made it work.
Measure first, buy last: how we keep our infrastructure lean
Most of our best infrastructure fixes were a measurement, not a purchase. The whole platform as code, the AWS price list as a design input.
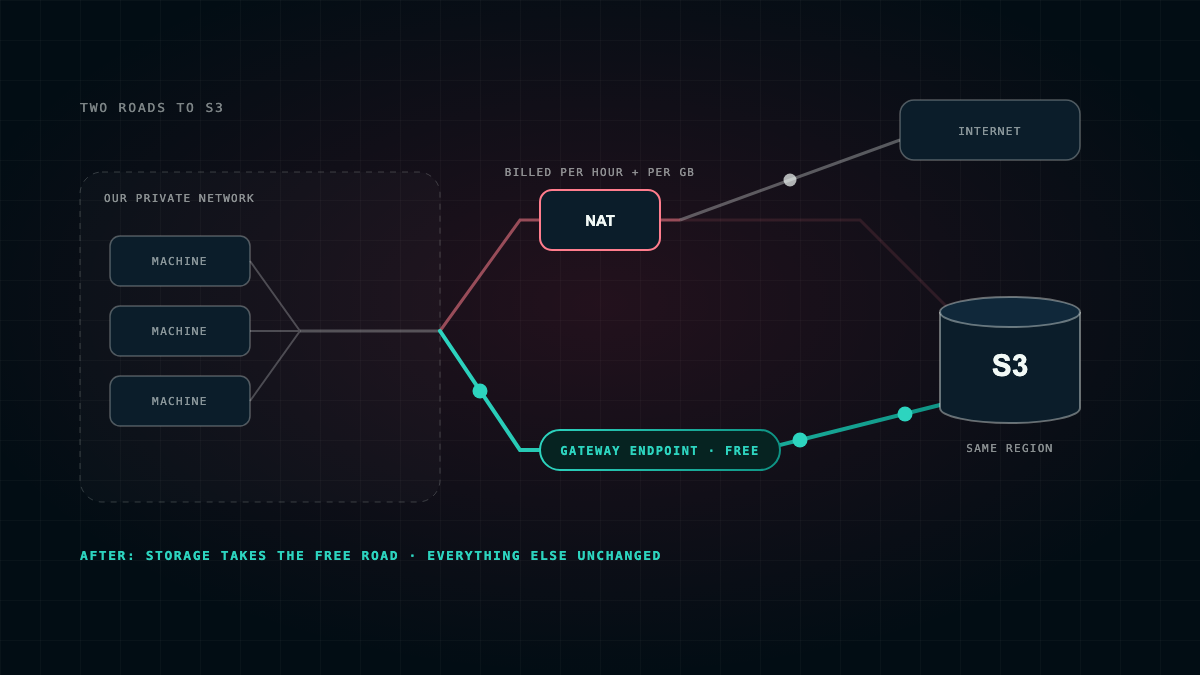
The free road to S3: moving storage traffic off our NAT gateway
Same-region S3 traffic is free, unless it goes through a NAT gateway. How a free gateway endpoint took logs, backups and downloads off the toll road.
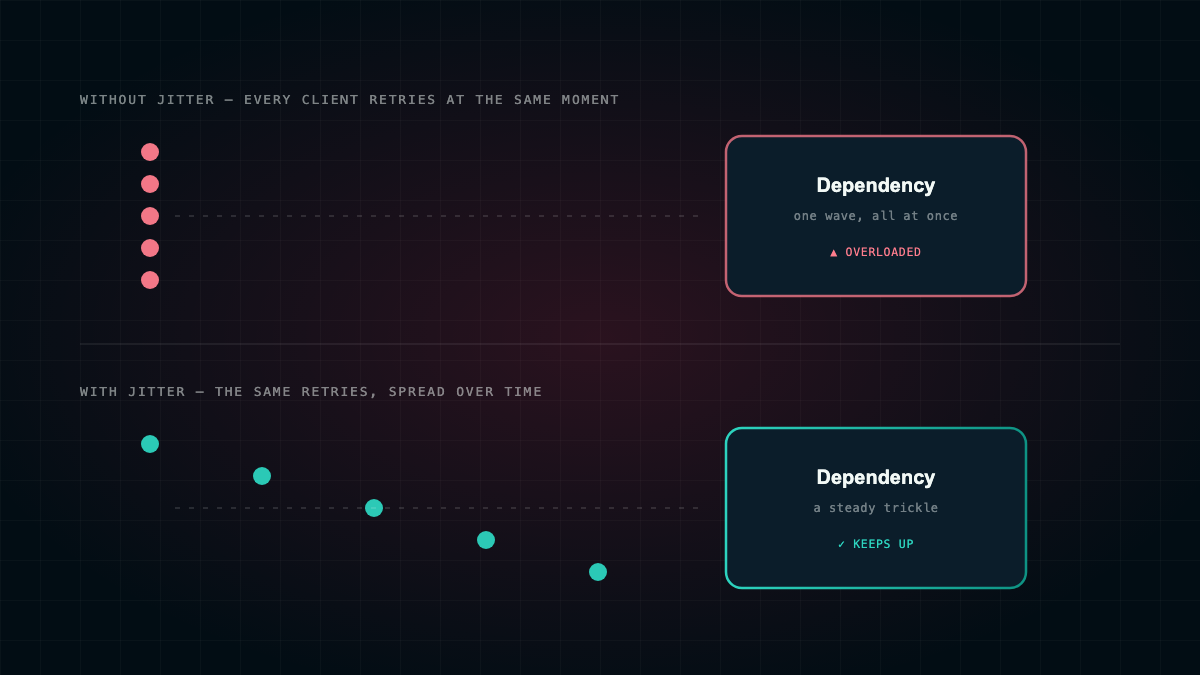
The jitter that never jittered: how a passing test hid a real bug
Our retry backoff had jitter, it ran on every publish, and it returned the same number every single time. The test passed. A postmortem.
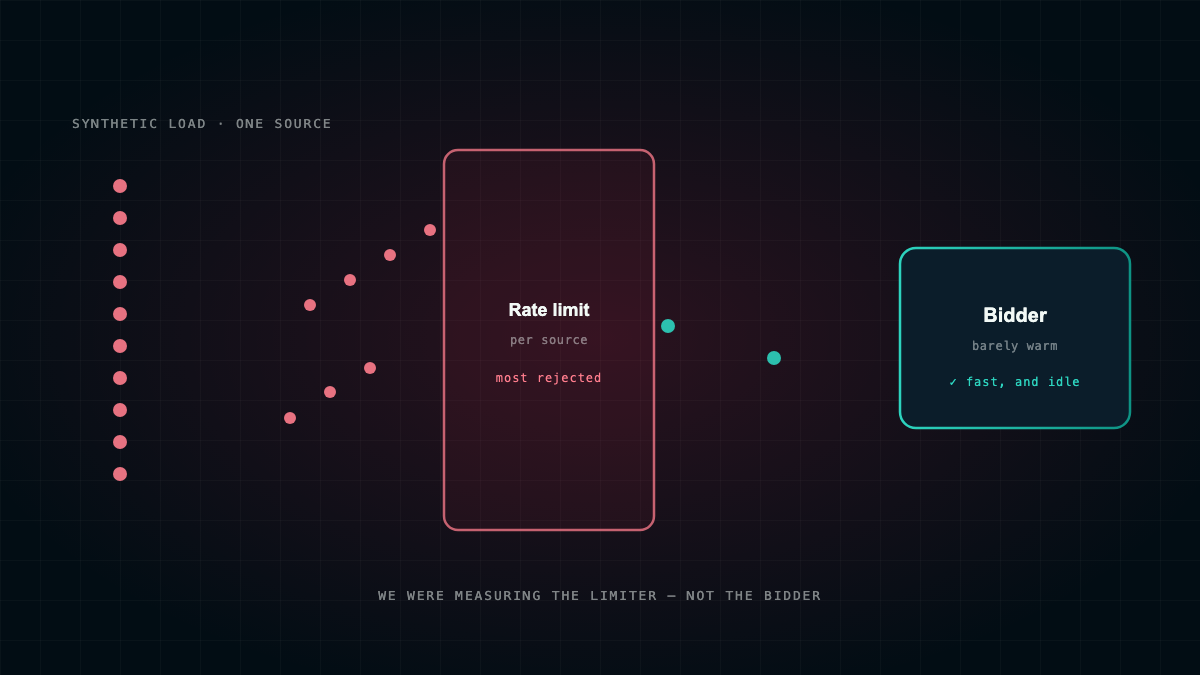
How we load test the bidder, and what our own test was hiding
Every pull request runs a load test before it can merge. Then we read our own report properly and found it was measuring the wrong thing.
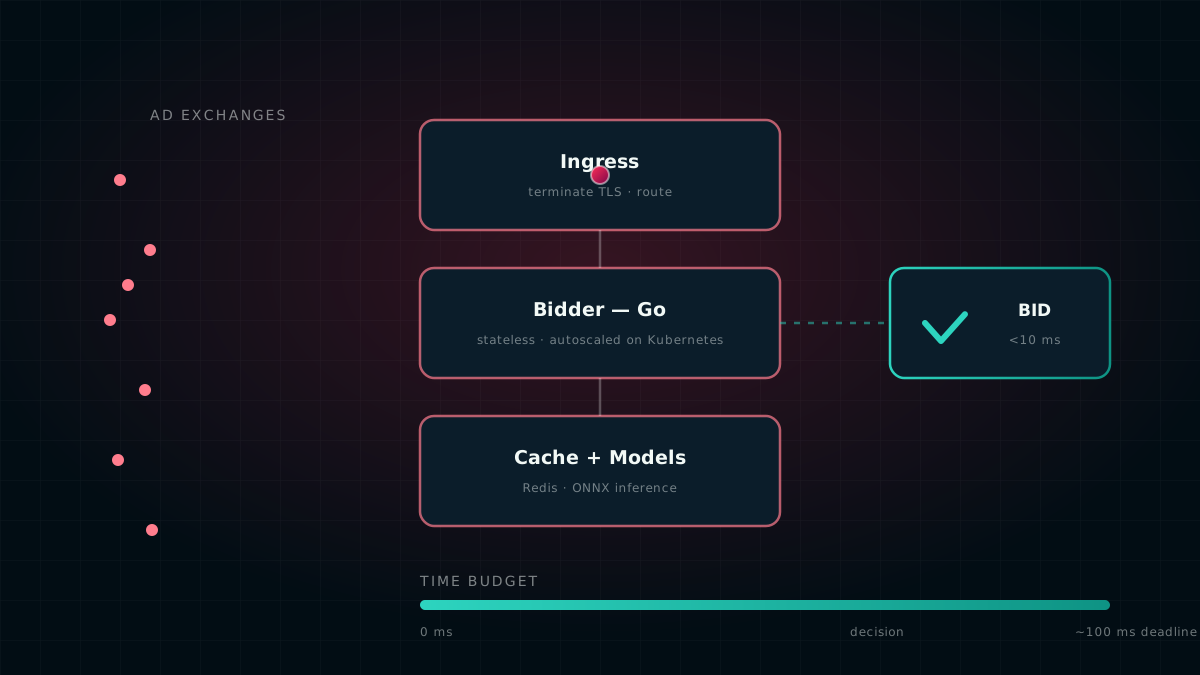
Inside AdZoic: the architecture behind millions of ad decisions a day
The stack, system design, security posture and scaling approach behind a real-time bidder handling close to ten million ad requests a day.
How machine learning decides what an impression is worth
Predictive bidding, bid shading and auto-optimization in plain English, and why explainable models matter.